
Free Preparation Discussions
 MENU

CrowdStrike CCFR-201b Exam Questions
- Topic 1: ATT&CK Frameworks: This domain covers understanding the MITRE ATT&CK framework and applying its tactics and techniques within Falcon to provide context to detections.
- Topic 2: Detection Analysis: This domain covers analyzing and triaging detections in Falcon, including interpreting dashboards, endpoint detections, contextual data, process views, prevalence, IOCs, and implementing hash management actions like blocking, allowlisting, and exclusions.
- Topic 3: Event Search: This domain focuses on performing advanced event searches from detections, refining searches using event actions, and distinguishing between commonly used event types.
- Topic 4: Event Investigation: This domain covers analyzing Process and Host Timelines, pivoting to Process Timeline or Process Explorer, and analyzing process relationships using Full Detection Details.
- Topic 5: Search Tools: This domain covers utilizing User Search, IP Search, Hash Search, Host Search, and Bulk Domain Search to gather intelligence during investigations.
- Topic 6: Real Time Response (RTR): This domain covers RTR technical capabilities, administrative settings, connecting to hosts, using RTR commands for remediation, utilizing custom scripts, setting up workflows, and reviewing audit logs.
Free CrowdStrike CCFR-201b Exam Actual Questions
Note: Premium Questions for CCFR-201b were last updated On Oct. 28, 2026 (see below)
What action is used when you want to save a prevention hash for later use?
According to theCrowdStrike Falcon Data Replicator (FDR) Add-on for Splunk Guide, the Always Block action allows you to block a file from executing on any host in your organization based on its hash value2.This action can be used to prevent known malicious files from running on your endpoints2.
How are processes on the same plane ordered (bottom 'VMTOOLSD.EXE' to top CMD.EXE')?
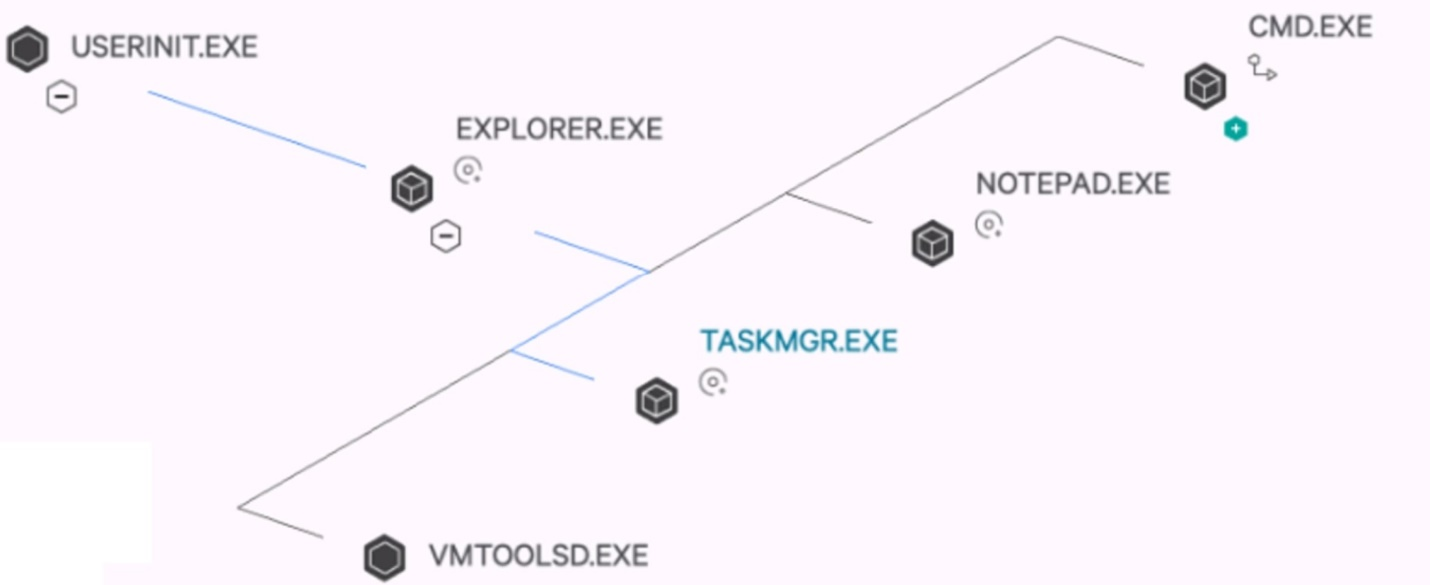
According to the CrowdStrike Falcon Devices Add-on for Splunk Installation and Configuration Guide v3.1.5+, the process tree view provides a visualization of program ancestry, which shows the parent-child and sibling relationships among the processes1.You can also see the event types and timestamps for each process1.The processes on the same plane are ordered by time started in descending order, meaning that the most recent process is at the bottom and the oldest process is at the top1.For example, in the image you sent me, CMD.EXE is the oldest process and VMTOOLSD.EXE is the most recent process on that plane1.
When examining a raw DNS request event, you see a field called ContextProcessld_decimal. What is the purpose of that field?
According to theCrowdStrike Falcon Devices Add-on for Splunk Installation and Configuration Guide v3.1.5+, the ContextProcessld_decimal field contains the decimal value of the process ID of the process that generated the event1.This field can be used to trace the process lineage and identify malicious or suspicious activities1.For a DNS request event, this field indicates which process made the DNS request1.
Which of the following is returned from the IP Search tool?
According to theCrowdStrike Falcon Devices Add-on for Splunk Installation and Configuration Guide v3.1.5+, the IP Search tool allows you to search for an IP address and view a summary of information from Falcon events that contain that IP address1.The summary includes the hostname, sensor ID, OS, country, city, ISP, ASN, and geolocation of the host that communicated with that IP address1.
You are notified by a third-party that a program may have redirected traffic to a malicious domain. Which Falcon page will assist you in searching for any domain request information related to this notice?
According to the [CrowdStrike website], the Investigate page is where you can search for and analyze various types of data collected by the Falcon platform, such as events, hosts, processes, hashes, domains, IPs, etc1.You can use various tools, such as Event Search, Host Search, Process Timeline, Hash Search, Bulk Domain Search, etc., to perform different types of searches and view the results in different ways1.If you want to search for any domain request information related to a notice from a third-party, you can use the Investigate page to do so1.For example, you can use the Bulk Domain Search tool to search for the malicious domain and see which hosts and processes communicated with it1.You can also use the Event Search tool to search for DNSRequest events that contain the malicious domain and see more details about the query and response1.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Donald Allen
1 month agoCharles Peterson
2 months agoSandra Johnson
2 months agoCrystal Thomas
3 months agoEmily Flores
3 months agoAshley Martinez
4 months agoChristopher Hill
4 months agoLaura Wilson
5 months agoJohn Nguyen
5 months agoOlivia Garcia
6 months agoAshley Peterson
6 months agoEmma Lewis
6 months agoMelissa Perez
6 months agoMonica Ramirez
6 months agoGerald Morris
6 months agoHarold Collins
6 months agoMicheal
7 months agoLizette
7 months agoRozella
7 months agoLenna
8 months agoGerman
8 months agoIzetta
8 months agoGalen
9 months agoMiriam
9 months agoGiovanna
9 months agoNoemi
9 months agoRodolfo
10 months agoJade
10 months ago