
Free Preparation Discussions
 MENU

CompTIA CS0-003 Exam Questions
Free CompTIA CS0-003 Exam Actual Questions
Note: Premium Questions for CS0-003 were last updated On Oct. 18, 2026 (see below)
A security analyst reviews the following extract of a vulnerability scan that was performed against the web server:
Which of the following recommendations should the security analyst provide to harden the web server?
The vulnerability scan shows that the version information is visible in the http-server-header, which can be exploited by attackers to identify vulnerabilities specific to that version. Removing or obfuscating this information can enhance security.
A security analyst identifies a device on which different malware was detected multiple times, even after the systems were scanned and cleaned several times. Which of the following actions would be most effective to ensure the device does not have residual malware?
Reimaging the device is the most effective way to eliminate persistent malware because some sophisticated malware, such as rootkits and firmware-level threats, can survive traditional scans and removals.
If a system keeps getting reinfected after cleaning, it may indicate a deeply embedded persistent threat, possibly in:
The Master Boot Record (MBR) or EFI firmware.
A compromised system restore point.
A hidden backdoor left by the malware.
Why Not Other Options?
A (Update and scan in safe mode) Might help, but if malware is persistent, it will likely return.
C (Upgrade OS) Does not necessarily remove malware; some malware survives OS upgrades.
D (Secondary scanner) Useful for detection but does not guarantee complete removal.
Best Practice:
Replace the hard drive to eliminate firmware-level infections.
Reimage the system from a known-good source.
Update the OS and security patches before reconnecting to the network.
During the log analysis phase, the following suspicious command is detected-
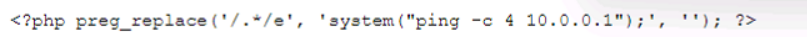
Which of the following is being attempted?
RCE stands for remote code execution, which is a type of attack that allows an attacker to execute arbitrary commands on a target system. The suspicious command in the question is an example of RCE, as it tries to download and execute a malicious file from a remote server using the wget and chmod commands. A buffer overflow is a type of vulnerability that occurs when a program writes more data to a memory buffer than it can hold, potentially overwriting other memory locations and corrupting the program's execution. ICMP tunneling is a technique that uses ICMP packets to encapsulate and transmit data that would normally be blocked by firewalls or filters.A smurf attack is a type of DDoS attack that floods a network with ICMP echo requests, causing all devices on the network to reply and generate a large amount of traffic. Verified Reference:What Is Buffer Overflow? Attacks, Types & Vulnerabilities - Fortinet1,What Is a Smurf Attack? Smurf DDoS Attack | Fortinet2,exploit - Interpreting CVE ratings: Buffer Overflow vs. Denial of ...3
A disgruntled open-source developer has decided to sabotage a code repository with a logic bomb that will act as a wiper. Which of the following parts of the Cyber Kill Chain does this act exhibit?
Weaponization is the stage of the Cyber Kill Chain where the attacker creates or modifies a malicious payload to use against a target. In this case, the disgruntled open-source developer has created a logic bomb that will act as a wiper, which is a type of malware that destroys data on a system. This is an example of weaponization, as the developer has prepared a cyberweapon to sabotage the code repository.
Cyber Kill Chain | Lockheed Martin, which states: ''In the weaponization step, the adversary creates remote access malware weapon, such as a virus or worm, tailored to one or more vulnerabilities.''
The Cyber Kill Chain: The Seven Steps of a Cyberattack - EC-Council, which states: ''In the weaponization stage, all of the attacker's preparatory work culminates in the creation of malware to be used against an identified target.''
What is the Cyber Kill Chain? Introduction Guide - CrowdStrike, which states: ''Weaponization: The attacker creates a malicious payload that will be delivered to the target.''
A Chief Information Security Officer (CISO) is concerned that a specific threat actor who is known to target the company's business type may be able to breach the network and remain inside of it for an extended period of time.
Which of the following techniques should be performed to meet the CISO's goals?
The correct answer is B. Adversary emulation.
Adversary emulation is a technique that involves mimicking the tactics, techniques, and procedures (TTPs) of a specific threat actor or group to test the effectiveness of the security controls and incident response capabilities of an organization1. Adversary emulation can help identify and address the gaps and weaknesses in the security posture of an organization, as well as improve the readiness and skills of the security team. Adversary emulation can also help measure the dwell time, which is the duration that a threat actor remains undetected inside the network2.
The other options are not the best techniques to meet the CISO's goals. Vulnerability scanning (A) is a technique that involves scanning the network and systems for known vulnerabilities, but it does not simulate a real attack or test the incident response capabilities. Passive discovery is a technique that involves collecting information about the network and systems without sending any packets or probes, but it does not identify or exploit any vulnerabilities or test the security controls. Bug bounty (D) is a program that involves rewarding external researchers or hackers for finding and reporting vulnerabilities in an organization's systems or applications, but it does not focus on a specific threat actor or group.
- Select Question Types you want
- Set your Desired Pass Percentage
- Allocate Time (Hours : Minutes)
- Create Multiple Practice tests with Limited Questions
- Customer Support
Susan Ramirez
1 month agoSusan Evans
2 months agoJames Bell
3 months agoDennis Brown
4 months agoVulnerability Management Anderson
5 months agoSecurity Operations Taylor
3 months agoThreat Intelligence Johnson
3 months agoElizabeth Nelson
5 months agoVulnerability Management Garcia
6 months agoSecurity Operations Brown
4 months agoKevin Murphy
6 months agoMelissa Wright
6 months agoJason Wright
6 months agoStephanie Collins
5 months agoJohn Stewart
5 months agoElizabeth Flores
6 months agoChanel
7 months agoColene
7 months agoJustine
7 months agoCarey
7 months agoMaurine
8 months agoErick
8 months agoMalinda
8 months agoReita
9 months agoPhyliss
9 months agoJaclyn
9 months agoMaurine
9 months agoHelene
10 months agoGeraldine
10 months agoMilly
10 months agoWilda
10 months agoMicheline
11 months agoAileen
11 months agoTeddy
11 months agoLuther
11 months agoJunita
12 months agoLazaro
12 months agoWava
1 year agoFreeman
1 year agoDominga
1 year agoLouvenia
1 year agoDelisa
1 year agoColby
1 year agoLeota
1 year agoHyman
1 year agoTheola
1 year agoArthur
1 year agoMa
1 year agoLashon
1 year agoSamira
1 year agoJoanna
1 year agoDelfina
1 year agoBilli
2 years agoRex
2 years agoKris
2 years agoDomitila
2 years agoJamal
2 years agoVivan
2 years agoMartina
2 years agoWerner
2 years agoLynelle
2 years agoMichal
2 years agoDesiree
2 years agoAnnamae
2 years agoValda
2 years agoMarshall
2 years agoKatheryn
2 years agoStanford
2 years agoLaurel
2 years agoPortia
2 years agoErin
2 years agoTamala
2 years agoEdison
2 years agoJohnetta
2 years agoCletus
2 years agoTheodora
2 years agoCora
2 years agoWillow
2 years agoRikki
2 years agoMelissa
2 years agoLavonna
2 years agoDerrick
2 years agoCristen
2 years agoHillary
2 years agoCasie
2 years agoArmando
2 years agoAshanti
2 years agoAileen
2 years agoAlberto
2 years agoNovella
2 years agoCarlee
2 years agoCristen
2 years agoBrandon
2 years agofelvaa
2 years agoalexa
2 years agoNathon
2 years agomelvin
2 years agoMark james
2 years agoAmmie
2 years ago