
 MENU

Refer to the exhibit.
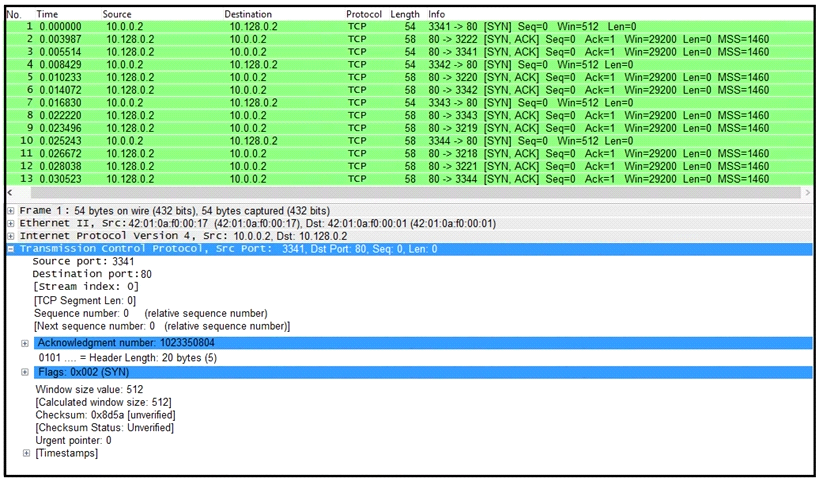
What is the threat in this Wireshark traffic capture?
Suggested Answer: D
Get Premium 350-201 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
12 comments · newest first
WI
Willard
3 months ago
Option C makes sense too. Multiple targets from one source is suspicious.
JU
Julie
3 months ago
I feel option D is more likely. Single source targeting a single IP.
LI
Lilli
3 months ago
I think it's option A. SYN flood attacks are common.
OT
Otis
3 months ago
Really? I thought SYN floods were less common now.
AS
Asha
4 months ago
I agree, D seems right.
RE
Remedios
4 months ago
Wait, isn't that just normal traffic?
TH
Theron
5 months ago
I think it's option D for sure.
LI
Lina
6 months ago
Definitely looks like a SYN flood attack.
JA
Jarvis
6 months ago
I keep mixing up the definitions of SYN and ACK floods. I guess I need to review that section again before making a choice.
BR
Brandon
6 months ago
I practiced a similar question last week, and I think the key is to identify the source and destination patterns. Could it be option C?
DO
Dortha
7 months ago
I'm not entirely sure, but I feel like a high rate of SYN packets from multiple sources might indicate a distributed attack, which could be option A.
CA
Carol
7 months ago
I remember we discussed SYN floods in class, so I think option D could be the right answer.