
 MENU

Refer to the exhibit.
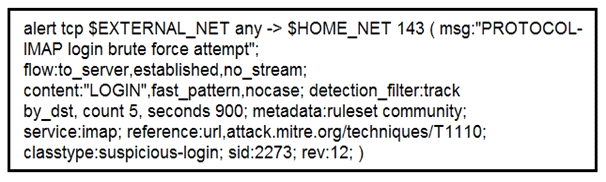
IDS is producing an increased amount of false positive events about brute force attempts on the organization's mail server. How should the Snort rule be modified to improve performance?
Suggested Answer: B
Get Premium 350-201 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
8 comments · newest first
GA
Gaston
12 months ago
Wait, are we really getting false positives from our own mail server? That's wild!
ME
Melynda
12 months ago
I disagree, tracking the source IP won't solve the false positive issue.
LE
Leontine
1 year ago
Changing the rule to case sensitive could help reduce false positives.
KA
Katlyn
1 year ago
Blocking internal IPs seems like a quick fix, but is it really effective?
RO
Rodrigo
1 year ago
I think tuning the count and seconds threshold is key!
QU
Quentin
1 year ago
Okay, let me see. I think the key here is that the question is asking about a system that guarantees the coherence of information security. That sounds like it's referring to a management or governance framework, not a specific technology. I'll go with A.
GE
Gearldine
1 year ago
Ah, I see. Restricting the general journal to only allow ledger-type transactions should work. I'm confident this solution will meet the client's needs.
SH
Shonda
1 year ago
Okay, I've got this. A relational database domain is the set of permissible values for an attribute in a table. So it's option B - a set of permissible tuple values. I'm confident that's the right answer.