
 MENU

Refer to the exhibit.
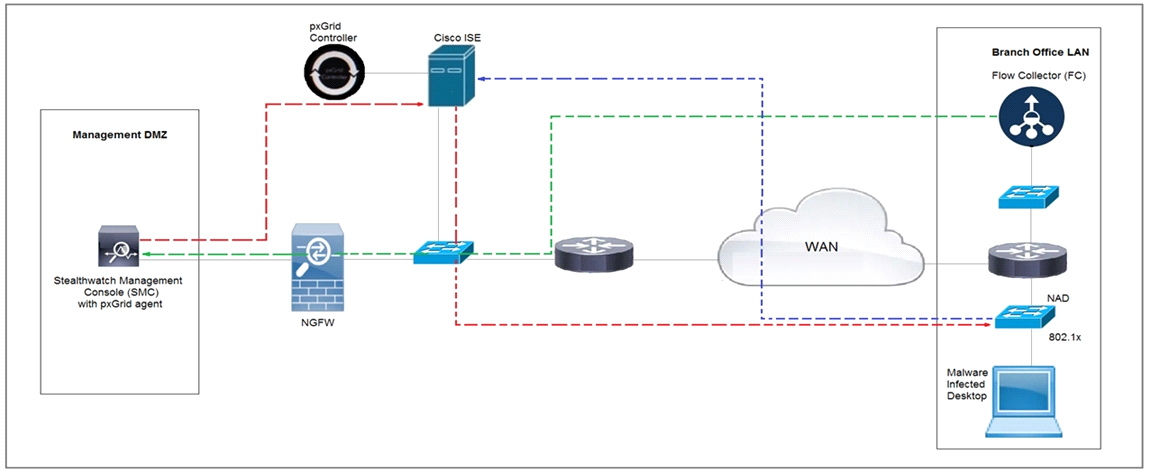
Cisco Rapid Threat Containment using Cisco Secure Network Analytics (Stealthwatch) and ISE detects the threat of malware-infected 802.1x authenticated endpoints and places that endpoint into a Quarantine VLAN using Adaptive Network Control policy. Which telemetry feeds were correlated with SMC to identify the malware?
Suggested Answer: B
Get Premium 350-201 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
9 comments · newest first
DA
Dalene
12 months ago
I thought it was C at first, but now I'm leaning towards A.
BL
Blondell
12 months ago
B could be a contender too, but A feels right.
TA
Tamar
1 year ago
Wait, how can they use SNMP for malware detection? Seems off.
MA
Marleen
1 year ago
Totally agree with A! Makes the most sense.
RA
Rashad
1 year ago
I think it's A, NetFlow and event data.
RI
Richelle
1 year ago
Okay, I've got this. Snapshots are typically used for data backup, restoration, and copying, so I'm pretty confident that A, B, and C are the correct answers here. I'll double-check, but I think I can nail this one.
KA
Katina
1 year ago
Hmm, I'm a little unsure about the exact details of what's included in a Linux distribution. I'll have to think this through carefully.
NA
Nakisha
1 year ago
The key here is understanding how server hardware types are defined and managed in HPE OneView. Option D sounds like the most logical answer - the server hardware type is automatically created when a new server is added to the environment.
HU
Hui
1 year ago
Hmm, I'm not too familiar with ANOVA analysis. I'll need to review my notes on how to approach these types of questions.