
 MENU

Refer to the exhibit.
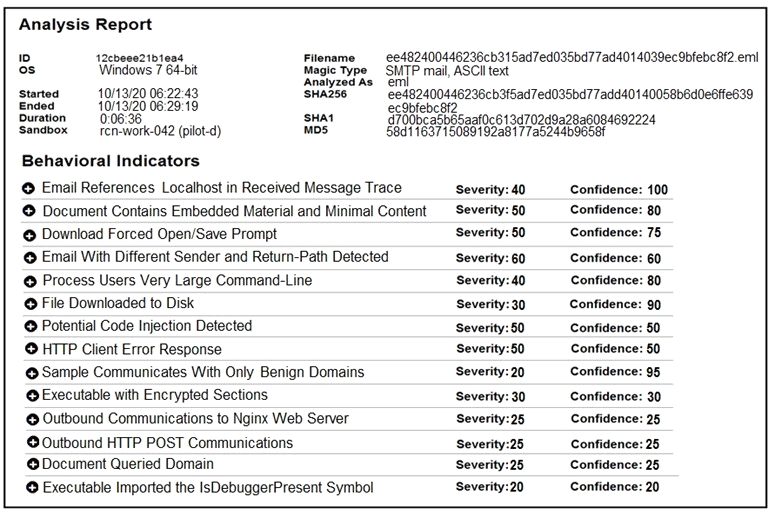
Cisco Advanced Malware Protection installed on an end-user desktop automatically submitted a low prevalence file to the Threat Grid analysis engine. What should be concluded from this report?
Suggested Answer: B
Get Premium 350-201 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
17 comments · newest first
AL
Alita
1 month ago
D is the safest bet. No malicious activity means we can relax.
ED
Edison
1 month ago
I vote for C. High scores mean we should investigate further.
JA
Jamal
1 month ago
A seems unlikely. If files were modified, we'd see more alerts.
VI
Vincenza
2 months ago
I feel like A is too extreme. High threat scores with modified files?
SH
Shelba
2 months ago
C is possible, but I lean towards D. Low prevalence suggests safety.
PA
Pamela
2 months ago
But what if it's C? High threat scores could indicate something serious.
JU
Justine
2 months ago
I agree, D makes sense. No malicious activity detected.
ME
Melodie
2 months ago
I think it's D. Low threat scores mean no real danger.
HE
Helaine
2 months ago
Wait, how can they submit a file if there's no malicious activity?
AM
Amber
3 months ago
I agree, D makes the most sense. Low threat and no activity.
IV
Ivette
3 months ago
Definitely leaning towards option D here. No malicious activity detected.
LO
Louis
3 months ago
I doubt that! Low scores but still submitting files? Seems fishy.
AS
Ashanti
3 months ago
Looks like the threat scores are low, so probably no big deal.
ME
Melissia
3 months ago
I recall that low prevalence doesn't always mean safe, but it could lean towards D. Still, I’m a bit confused about the threat scores.
SA
Sabina
3 months ago
I'm not entirely sure, but I feel like if it was ransomware, the threat scores would be high. So maybe A or C?
DE
Detra
4 months ago
I think I saw a similar question where low threat scores meant no malicious activity was detected. Could it be D again?
DE
Denae
4 months ago
I remember studying that low prevalence files usually indicate less risk, so maybe D is the right choice?