
 MENU

Refer to the exhibit.
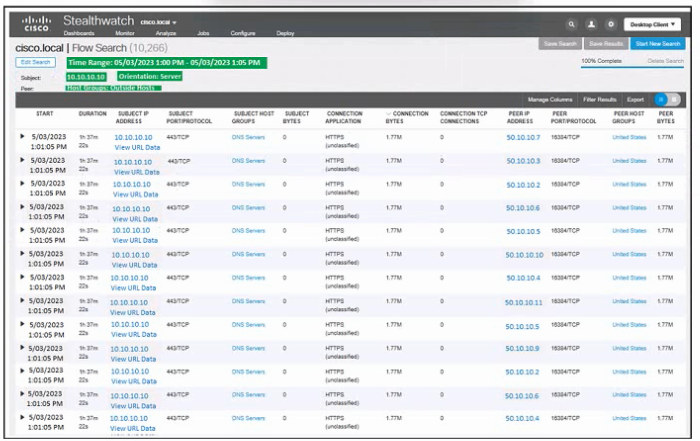
Refer to the exhibit. An engineer must troubleshoot an incident by using Cisco Secure Cloud Analytics. What is the cause of the issue?
Suggested Answer: A
Get Premium 300-740 Questions
as Interactive Web-Based Practice Test or PDF
Real Exam Format
Detailed Explanations
Instant Access
Get Your Practice Test
25 comments · newest first
GE
Gertude
9 months ago
Wait, a DoS attack from an internal IP? Really?
MO
Mollie
9 months ago
I think it's the Ping of Death attack.
CH
Charlesetta
10 months ago
Definitely a DoS attack from inside the network.
RO
Ronald
10 months ago
Looks like a SYN flood attack to me.
LU
Lucina
11 months ago
Not sure about that, TCP fingerprinting seems off.
VI
Victor
11 months ago
TCP fingerprinting seems like a less likely cause, but I might be mixing it up with other types of network scans we covered.
JU
Jutta
11 months ago
I feel like the Ping of Death attack was mentioned in our last session, but I can't remember if it applies to this scenario.
CR
Crissy
11 months ago
I think the DoS attack option sounds familiar from practice questions, but I can't recall the specifics.
DU
Dulce
12 months ago
I remember studying SYN flood attacks, but I'm not sure if that's the right answer here.
YO
Youlanda
12 months ago
The Ping of Death attack option seems plausible, but I'm not sure if that's the right answer. I'll need to think through the details of each attack type.
DE
Devorah
1 year ago
I'm a bit confused by the different network ranges mentioned. I'll need to double-check my understanding of the topology and IP addressing scheme.
CL
Clement
1 year ago
Okay, I think I see a SYN flood attack targeting the DNS server. That seems like the most likely cause based on the information provided.
FR
France
1 year ago
The exhibit shows some suspicious activity, but I'm not sure which type of attack is happening. I'll need to review the options carefully.
JE
Jerry
1 year ago
This looks like a network security issue, so I'll need to carefully analyze the traffic patterns and IP addresses to determine the cause.
PE
Pearlene
1 year ago
Hold up, what if it's just some good old-fashioned TCP fingerprinting? That 50.10.10.0/24 network is looking pretty suspicious to me.
EL
Elke
1 year ago
Hmm, I'm not so sure. The Ping of Death attack seems like a better fit. That 10.10.10.10 host is definitely the target.
CA
Cassie
10 months ago
I’m leaning towards TCP fingerprinting. It’s stealthy and can gather info without being obvious.
MA
Marisha
10 months ago
True, but a DoS from an internal IP could be a bigger issue for the network.
SU
Sueann
10 months ago
But the Ping of Death could really disrupt that host. It’s a classic attack.
CA
Carla
11 months ago
I think the SYN flood attack is more likely. It targets the DNS server directly.
VA
Val
1 year ago
I disagree, I believe it's a DoS attack toward the 50.10.10.0/24 network from an internal IP address.
AL
Allene
1 year ago
Nah, it's got to be a DoS attack on the 50.10.10.0/24 network. That's the most logical choice here.
YO
Yolando
1 year ago
I think it's a SYN flood attack toward the DNS server. The IP address 10.10.10.10 is a giveaway.
NA
Nathan
1 year ago
User 1: I agree, the IP address 10.10.10.10 points to a SYN flood attack.
YV
Yvonne
1 year ago
I think the cause of the issue is a SYN flood attack toward the DNS server with IP address 10.10.10.10.