Free Preparation Discussions
 MENU

Free Cisco 200-201 Exam Dumps October 2026
Here you can find all the free questions related with Cisco Understanding Cisco Cybersecurity Operations Fundamentals (200-201) exam. You can also find on this page links to recently updated premium files with which you can practice for actual Cisco Understanding Cisco Cybersecurity Operations Fundamentals Exam. These premium versions are provided as 200-201 exam practice tests, both as desktop software and browser based application, you can use whatever suits your style. Feel free to try the Understanding Cisco Cybersecurity Operations Fundamentals Exam premium files for free, Good luck with your Cisco Understanding Cisco Cybersecurity Operations Fundamentals Exam.What is the purpose of a host-based intrusion detection system (HIDS)?
MultipleChoice
An analyst see that this security alert "Default-Botnet-Communication-Detection-By-Endpoint" has been raised from the IPS. The analyst checks and finds that an endpoint communicates to the C&C. How must an impact from this event be categorized?
OptionsMultipleChoice
Which access control should a chief information security officer Choose to protect extremely sensitive data categorized at various levels of confidentiality?
OptionsMultipleChoice
What is the difference between an attack vector and an attack surface?
OptionsMultipleChoice
Refer to the exhibit.
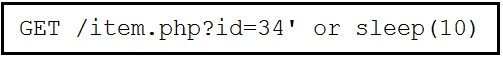
This request was sent to a web application server driven by a database. Which type of web server attack is represented?
OptionsMultipleChoice
What is an advantage of symmetric over asymmetric encryption?
OptionsMultipleChoice
Which list identifies the information that the client sends to the server in the negotiation phase of the TLS handshake?
OptionsMultipleChoice
A suspicious user opened a connection from a compromised host inside an organization. Traffic was going through a router and the network administrator was able to identify this flow. The admin was following 5-tuple to collect needed dat
a. Which information was gathered based on this approach?
OptionsMultipleChoice
Refer to the exhibit. Where is the executable file?
OptionsMultipleChoice
Refer to the exhibit. An employee received an email from an unknown sender with an attachment and reported it as a phishing attempt. An engineer uploaded the file to Cuckoo for further analysis. What should an engineer interpret from the provided Cuckoo report?
Options