Deal of The Day! Hurry Up, Grab the Special Discount - Save 25% - Ends In 00:00:00 Coupon code: SAVE25

Free Preparation Discussions
 MENU

Adobe AD0-E704 Exam - Topic 8 Question 9 Discussion
Actual exam question for
Adobe's
AD0-E704 exam
Question #: 9
Topic #: 8
[All AD0-E704 Questions]
Topic #: 8
You are programmatically creating a customer EAV attribute and want to add it to the customer segment's condition options. How do you do this?
A)
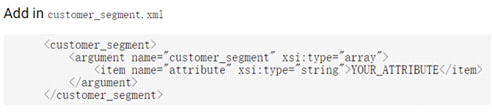
B)
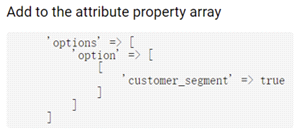
C)
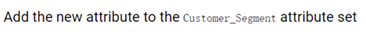
D)

Suggested Answer:
B
Ilda
10 months agoKimberely
11 months agoDorothy
11 months agoKatina
11 months agoMadelyn
11 months agoAlbina
11 months agoStephaine
11 months agoChantell
11 months agoKristal
11 months agoShannon
12 months agoTom
12 months agoAvery
12 months ago